Paraxial.io 2.13.0 Scans Elixir for Known Vulnerabilities
Paraxial.io, 2026-11-02
On October 29, 2026, the Elixir team released new patch versions to fix several CVEs, including CPU exhaustion in URI.parse/1 (CVE-2026-109821), oversized integers in the JSON decoder (CVE-2026-115274), and mix deps.partition on multi-user systems (CVE-2026-97209). Make sure you are running one of: 1.18.6, 1.19.7, or 1.20.5.
Paraxial.io for Elixir version 2.13.0 adds Elixir vulnerability scanning to mix paraxial.scan. Version 2.12.0 started checking the Erlang/OTP runtime. This release does the same for Elixir itself: the scan now reports the known security advisories that affect the Elixir version your project is running on, alongside the existing OTP, hex dependency, license, and Sobelow results.
Paraxial.io for Ruby 1.5.0 Finds Regexps Built From User Input
Paraxial.io, 2026-10-23
Today the Ruby team released Ruby 4.0.9, 3.4.12, and 3.3.13, fixing memory safety bugs in the regular expression engine. GitLab found that specially crafted patterns could corrupt memory while Ruby compiles them, and used that for remote code execution on GitLab servers. The four ids to track are CVE-2026-89078, CVE-2026-93577, CVE-2026-97229, and CVE-2026-110264, all assigned by GitLab, because the Ruby project has not requested its own.
Paraxial.io for Ruby version 1.5.0 is out today with a new cop, Paraxial/DynamicRegexp, which finds the code in your application that reaches these bugs.
What the eMudhra CA Compromise Means for Elixir Developers
Michael Lubas, 2026-10-21
The eMudhra Intermediate CA Compromise site details how the private keys of eight eMudhra intermediate CA certificates are not secret. You may have seen reporting by now that one of the private keys used was the integer ‘4’. In summary, eMudhra did not generate their private keys correctly and now anyone on the internet can make a certificate for any domain, and many non-browser TLS clients, including Erlang’s :ssl, will accept it. Firefox, Chrome, Apple and Microsoft now block the intermediates with their own revocation data. Developers need to update their software and packages.
If you are responsible for a deployed Elixir/Phoenix application, this means an attacker who sits between your application and an intended destination (such as an API server) can impersonate that destination, and read and change all traffic between them. To divert the traffic, the attacker needs a DNS hijack, a BGP hijack, a compromised proxy, or one compromised host in your network. Before this incident, the lack of a trusted certificate usually stopped these attacks. That protection is gone, hence the current rush to patch this vulnerability.
If you are an Elixir developer, this means you must update every CA store your application uses.
Paraxial.io 2.12.0 Scans Erlang/OTP for Known Vulnerabilities
Paraxial.io, 2026-10-19
Paraxial.io for Elixir version 2.12.0 adds Erlang/OTP vulnerability scanning to mix paraxial.scan. The scan now reports the known security advisories that affect the Erlang/OTP version your project is running on, alongside the existing hex dependency, license, and Sobelow results. Here is everything you need to use it.
Avandra Engages Paraxial.io for Medical Imaging Intelligence Penetration Testing
Paraxial.io, 2026-10-07
Every year billions of medical images are produced: CT scans, X-rays, MRIs, echocardiograms. Once the image is created, the goal is to effectively use it to treat the patient correctly, yet this data often goes completely dark the day after it is read. It sits in hospital archives, expensive to store, impossible to search, and invisible to researchers and doctors working to cure diseases and treat patients.
Avandra Imaging is solving this problem by powering the future of Imaging Intelligence. Its image exchange products run inside IDNs, community hospitals, specialty clinics, and outpatient imaging centers nationwide — and that same on-site footprint powers a data platform that indexes existing PACS and VNA archives and de-identifies studies before they leave the health system, turning data that used to go dark into curated, privacy-protected imaging data for research and modern artificial intelligence.
Paraxial.io was honored to be selected by Avandra for a penetration test of its information systems. Avandra uses Elixir, a language Paraxial.io has extensive security experience with, to ensure highly reliable uptime and system access for customers. For example, Paraxial.io open-sourced the first runtime application self-protection (RASP) library for Elixir, to prevent remote code execution (RCE) vulnerabilities in critical systems.
Thank You ElixirConf US 2026
Michael Lubas, 2026-09-17
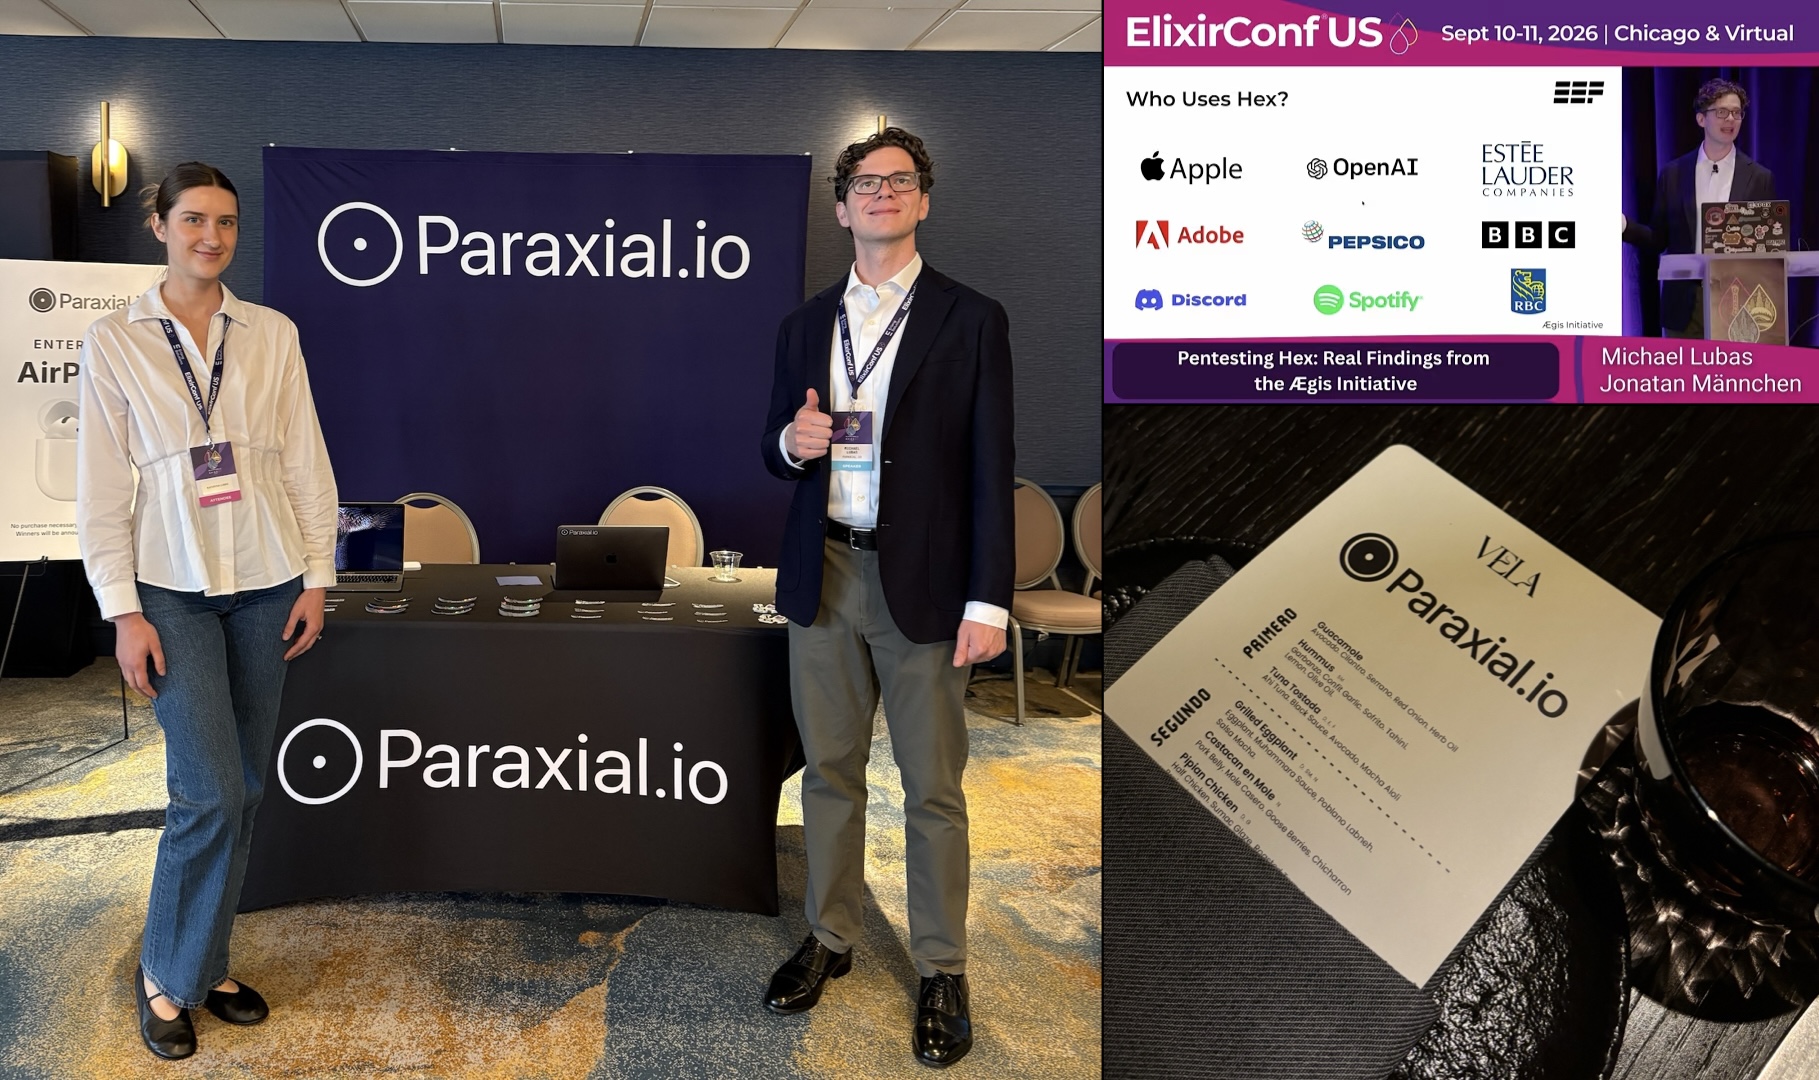
Thank you everyone who attended ElixirConf US 2026 this year. Being able to connect with Paraxial.io customers and users in-person was incredible, and I am grateful for the opportunity to help secure the important work everyone is doing with Elixir.
My talk from the conference, Pentesting Hex: Real Findings from the Ægis Initiative is up on YouTube now! https://www.youtube.com/watch?v=_fER9bzlSOE
The talk covers the security audit of the Hex package manager that Paraxial.io performed under the Erlang Ecosystem Foundation’s Ægis Initiative, funded by Alpha-Omega. If you want the written version, see Securing Hex, the Backbone of the Elixir Ecosystem, and the full public report.
Security Vendor's AI Best Practices Labels Critical Elixir RCE Safe
Michael Lubas, 2026-08-03
Security firm Safeguard.sh published an Elixir guide last month (July 2026) that tells developers to defend against untrusted deserialization with the following:
Securing Hex, the Backbone of the Elixir Ecosystem
Michael Lubas, 2026-04-09
The Erlang Ecosystem Foundation’s (EEF) Security Working Group prudently launched the Ægis Initiative in 2025 to improve supply chain integrity for the overall Erlang and Elixir ecosystem. Jonatan Männchen (EEF CISO) and Alistair Woodman (EEF Board President) are the project leads, who have worked tirelessly to ensure the security and health of this critical infrastructure. The Supply Chain Security Audit project under Ægis scoped out a full assessment of the Hex Package Manager and related software. Hex boasts over 14 billion all time downloads, over 24,000 available packages, and is a vital asset for all companies using the Elixir, Erlang, and Gleam languages. Two firms were selected to perform this audit: Paraxial.io and zentrust partners GmbH. The Hex project has published an excellent summary of the work on their blog.
The funding for this work was generously provided by Alpha-Omega, an associated project of the Open Source Security Foundation (OpenSSF) and The Linux Foundation. Funding for Alpha-Omega is provided by Anthropic, AWS, Citi, GitHub, Google, Google DeepMind, Microsoft, and OpenAI. These organizations are deeply committed to improving the security of the open source ecosystem, as shown by their real world action. Their financial support directly protects the foundation of our digital infrastructure. Paraxial.io was honored to be selected as a recipient of this grant, for the security assessment of Hex.
Paraxial.io Now Supports Req
Michael Lubas, 2026-03-19
Paraxial.io for Elixir version 2.9.0 adds support for Req as an HTTP client, alongside existing HTTPoison support. As the Elixir ecosystem continues to standardize around Req, this update ensures Paraxial.io integrates smoothly into modern projects.
No additional configuration is required. Paraxial.io detects which HTTP client is available at runtime and uses it automatically. If Req is installed, it takes priority. If only HTTPoison is present, it will be used as before. If both are available, Req is preferred.
How Killswitch Uses Paraxial.io to Protect Client Estates
Paraxial.io, 2026-03-04
Killswitch gives families peace of mind. Users upload their most important documents like wills, insurance policies, property records, and account credentials, designate beneficiaries, and set a check-in schedule. If they ever miss one, the right people automatically get secure access to exactly what they need. No lawyers, no probate delays, no scrambling during the hardest moments. It’s the kind of protection that used to require expensive estate planning.
That promise comes with an unusually high security bar. Being trusted with someone’s most sensitive documents means a breach isn’t just a data incident, it’s a potential catastrophe for real families. Founder Jacob Luetzow built Killswitch on a zero-knowledge architecture: files are encrypted in the browser before upload using AES-256-GCM, with keys derived from the user’s password. The server never sees plaintext. But zero-knowledge encryption doesn’t protect against credential stuffing, SQL injection, or code execution payloads hitting the app in production, which is where Paraxial.io comes in.
Why We Don't Run Your Code
Michael Lubas, 2025-09-05
A recent blog post from Kudelski Security opens strongly with “how we got remote code execution (RCE) on CodeRabbit’s production servers, leaked their API tokens and secrets, how we could have accessed their PostgreSQL database, and how we obtained read and write access to 1 million code repositories, including private ones”. The summary is:
Phoenix 1.8 Gets Official Security Documentation
Michael Lubas, 2025-06-18
Phoenix 1.8.0-rc was released in March 2025 to much excitement in the Elixir community. Highlights included daisyUI, enhancements to phx.gen.auth, and scopes to ensure strong access control. Given the security improvements in the first release candidate, it seems appropriate that the final release of Phoenix 1.8 will include official security documentation.
You can read the full text in the pull request above, the documentation covers the following OWASP Top 10 vulnerabilities in Phoenix applications:
Why GetThru uses Paraxial.io
Matt Silbernagel, 2025-06-09
At GetThru, we use Elixir to build peer-to-peer communication tools that help mission-driven organizations connect with people at scale. Our clients, ranging from advocacy groups to educational institutions, trust us to take security seriously, which we are committed to do.
That’s why we use Paraxial.io. It’s helped us improve our security posture, reduce engineering overhead, and meet the rigorous expectations of our customers, without getting in the way.
Why VC Funded Security Firms Miss a Critical Vulnerability
Michael Lubas, 2025-04-29
CVE-2025-32433, an Unauthenticated Remote Code Execution in Erlang/OTP SSH recently had every organization using Elixir asking the same question: Can a bad guy hack our internet facing web applications and cause a data breach? If you are responsible for the security of Elixir projects (which use the Erlang VM), and you are currently a customer of the legacy application security firms, you were likely disappointed with their inability to detect CVE-2025-32433. Why is it that firms specialized in application security will claim Elixir support, yet fail to deliver when the chips are down? The answer can be found by examining the incentive structure between investors and security vendors.
What the Critical Erlang SSH Vulnerability Means for Elixir Developers
Michael Lubas, 2025-04-17
CVE-2025-32433, an Unauthenticated Remote Code Execution in Erlang/OTP SSH was announced yesterday. From the description:
A serious vulnerability has been identified in the Erlang/OTP SSH server that may allow an attacker to perform unauthenticated remote code execution (RCE). By exploiting a flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without valid credentials.
How Paraxial.io Helps Developers Achieve 12 Key SOC 2 Controls
Michael Lubas, 2025-04-02
Developers use Paraxial.io to ensure their software is safe against cyberattacks. This protection is also required by many regulatory and compliance frameworks. System and Organization Controls 2 (SOC 2) was created by the American Institute of Certified Public Accountants (AICPA), and is a common requirement for SaaS businesses looking to sell into enterprise markets. Using Paraxial.io fulfills the following controls:
Ruby on Rails Security: Preventing Command Injection
Michael Lubas, 2025-03-14
In the taxonomy of security vulnerabilities, remote code execution (RCE) typically ranks as the most severe. A web application that is vulnerable to RCE can be exploited by an attacker, who gets the equivalent of production SSH access to the underlying web server. With this level of access the bad guy can:
Elixir and Phoenix Security Checklist: 11 Best Practices
Michael Lubas, 2025-02-11
Coding a web application in Elixir with the Phoenix framework gives you an incredibly solid base. Any security problems that occur are preventable, if you know what to watch out for. The list below is based on my own professional experience pentesting Elixir applications, and building a company to help developers with security. My goal is to help you avoid a data breach due to your project being hacked, each line item was selected with that consideration in mind.
The full list ranked in order of priority:
Introducing Paraxial.io 3.0
Michael Lubas, 2025-02-05
Today Paraxial.io 3.0 is live, a major upgrade to help developers with software security. Perhaps the best way to communicate how much has been accomplished is to list all the improvements shipped:
Paraxial.io Completes Security Audit of Oban Pro
Michael Lubas, 2025-01-29
Paraxial.io has completed a security audit of Oban Pro and Oban Web. The project contains a set of Elixir libraries used by Fortune 500 companies and leading startups to process background jobs and manage complex workflows. Paraxial.io was selected for this engagement because of our expertise with Elixir. Key findings:
Free Rails Security Scan by Paraxial.io
Michael Lubas, 2025-01-23
Every Ruby on Rails application exposed to the public internet will be attacked by hackers scanning for SQL injection, remote code execution, and similar vulnerabilities that lead to total system compromise. This guide will cover the most relevant threats and how to take advantage of free Rails security scanning by Paraxial.io.
Gem Shop: A Vulnerable Rails 8 App for Security Education
Michael Lubas, 2025-01-07
Gem Shop is an intentionally vulnerable Ruby on Rails 8 project for security education, with examples of SQL injection, cross site scripting (XSS), broken access control, and more. The application is a simple e-commerce site where users can shop for gemstones. Most people are familiar with online shopping today, so starting with this base students can learn how security issues occur in a Rails codebase. The project is open source and hosted on the Paraxial.io GitHub.
Many web developers are interested in security, and there are numerous resources online for learning about vulnerabilities in web applications, for example XSS. When teaching this subject I’ve found hands on labs to be the most effective way for students to understand the material. If a student is experienced with Ruby on Rails, and the lab exercise is a Rails project, they can focus more on understanding the security concept (XSS, CSRF, etc.) instead of deciphering a web framework they are not familiar with.
Introducing Paraxial.io Network Scanning
Michael Lubas, 2024-12-18
Paraxial.io can now continuously monitor your servers’ open ports and SSH settings. If you are hosting an application in a virtual private server (VPS), for example an AWS EC2 instance, this is a useful security check to ensure your server is not exposing sensitive internal software to the public internet.
The recent article Security Best Practices for Deploying Rails 8 on Linux with Kamal discussed how exposing Docker on port 2375 to the public internet will lead to your server getting hacked. Other common services you generally do not want to leave open:
Introducing Vulnerability Report Analytics in Paraxial.io
Michael Lubas, 2024-11-19
Across all the web applications in your organization, how many vulnerabilities are currently outstanding? Is this number increasing or decreasing over time? How many of those are critical severity, found in internet-facing projects? Paraxial.io helps engineers answer these questions. Today the Vulnerability Report feature of Paraxial.io is live in all accounts, providing a detailed breakdown of this data over time.
Ban Bots Scanning for Vulnerable WordPress with Paraxial.io
Michael Lubas, 2024-11-12
All web applications on the public internet will be targeted by automated malicious scanners. A common example is WordPress, due to how many sites use it, and the high number of exploitable bugs. If you have a Ruby or Elixir app, a malicious bot scanning for WordPress vulnerabilities does not pose a real threat, because the exploit being used will not work. There are several good reasons to still ban the offending IP:
Security Best Practices for Deploying Rails 8 on Linux with Kamal
Michael Lubas, 2024-11-05
The best advice I can give as an IT security professional on running your own server: just don’t. - How To Protect Your Linux Server From Hackers!, LiveOverflow
It’s more fun to be competent! - Rails World 2024 Keynote, David Heinemeier Hansson
Security is a Growth Center
Michael Lubas, 2024-10-14
How would a cybersecurity breach affect your startup’s growth? It is hard to imagine a positive outcome. The goal of a startup is to grow quickly, and ensuring the security of customer data keeps the momentum going. Every company today needs to prioritize security, yet there is a common misconception that security is a cost center, while sales and marketing are profit centers. Where does this idea come from?
“One of the biggest mistakes I have made during my career was coining the term profit center, around 1945. The truth is that inside the business, there are only cost centers. The only profit center is a customer whose check hasn’t bounced.” - Managing in the Next Society, Peter F. Drucker, 2002
Paraxial.io at Rails World 2024
Michael Lubas, 2024-09-30
Paraxial.io is a security company building a product targeted at developers. Our goal is to make securing your application as painless as possible. Naturally, building a good product requires connecting with users. Rails World 2024 was held in Toronto last week, and Paraxial.io was proud to sponsor the conference.
David’s keynote is up on YouTube and absolutely worth watching. A major theme in the presentation is that Rails as a project is intended to help developers start their web application, build features, and accomplish work. Rails is free, used by everyone from Fortune 500 companies to independent freelancers. No vendor lock-in, you have the freedom to use Rails with any hosting environment, from bare metal server to cloud provider, and the team has built some incredible tooling to support that goal.
Introducing Paraxial.io for Ruby on Rails
Michael Lubas, 2024-09-10
Ruby on Rails is a project that needs no introduction. Used at companies including Airbnb, Coinbase, Shopify, and GitHub, it is difficult to estimate the enormous contribution of Rails to the modern web. Started by David Heinemeier Hansson of 37signals, Rails has influenced most web frameworks currently in use. Today support for Ruby on Rails is live in Paraxial.io. Developers can now secure their Rails app with Paraxial.io, taking advantage of features including:
Secure Your Gigalixir App with Paraxial.io
Michael Lubas, 2024-08-27
Gigalixir is a popular Platform as a Service (PaaS) provider for Elixir applications, for good reason. The service was built from the ground up for Elixir developers, from individuals deploying their first application to businesses relying on the service for critical revenue generating applications. When it comes to securing an Elixir application, support from legacy security vendors is bad, and often requires mucking about with docker, installing an additional language (such as Java), and fails to secure applications hosted on a PaaS such as Gigalixir.
This article will walk through using Paraxial.io to secure an Elixir application running on Gigalixir. If you would like to follow along with your own app, both Gigalixir and Paraxial.io have free tiers, you can sign up here:
Ruby Support is Coming to Paraxial.io
Michael Lubas, 2024-07-31
Paraxial.io stops data breaches by helping developers ship secure applications. The key benefit is that you don’t need to be a security expert to ensure your app is safe, Paraxial.io makes the work simple, with features including:
Paraxial.io is Free for Elixir Developers
Michael Lubas, 2024-07-15
Paraxial.io helps developers ensure the project they are shipping is secure. Today you can use most Paraxial.io features for free (no credit card required) to ensure the security of your non-commercial work. What does this mean? Lets say you have a side project, hosted on the public internet, where people can create an account and share lists of media with their friends (books, podcasts, music, movies, etc). The security risk here seems low, but consider the following scenarios:
Elixir, Phoenix, and the OWASP Top 10
Michael Lubas, 2024-06-20
The OWASP Top 10 is a well known application security awareness document. When a developer working on internet-facing web applications decides to learn about security, OWASP is a frequently recommended source of information, with the Top 10 as the most famous project. The point of this article is to provide developers with enough context to understand the strengths and limitations of the Top 10 document. To properly engage with this subject, it is necessary to define a web application that is vulnerable to some security problems. This article will use the intentionally vulnerable Elixir and Phoenix project Potion Shop to explain how the Top 10 relates to real world security issues.
Announcing Phoenix LiveView Support in Paraxial.io
Michael Lubas, 2024-04-30
Phoenix LiveView has seen incredible adoption in the past few years, providing developers with the ability to ship real time web applications with minimal latency and bandwidth usage. Paraxial.io is the only security product with a strong Elixir focus, so a natural question is “Does Paraxial.io support LiveView”? The answer is yes!
Introducing the Paraxial.io Jira Integration
Michael Lubas, 2024-04-03
Jira is the industry leading project management tool used by security, engineering, and product teams. Today the Paraxial.io Jira integration is officially available. How does it work? Consider the following Paraxial.io finding:
How to Use Paraxial.io to Check If You Are Affected by the XZ Backdoor
Michael Lubas, 2024-03-30
TL;DR? Upgrade your Paraxial agent to 2.7.3 in mix. When you start your Elixir app, Paraxial.io will record the version of xz you are running in production, to be viewed in the site’s App Audit. 5.6.0 and 5.6.1 have the backdoor, other versions are safe.
XZ is a package used in most Linux distributions, meaning if you are running an Elixir/Phoenix web application on a Linux web server, you probably have it installed. A high severity backdoor was recently discovered in xz versions 5.6.0 and 5.6.1.
Paraxial.io at ElixirConf EU 2024
Michael Lubas, 2024-03-19
ElixirConf EU is happening on April 18th in Lisbon, Portugal. Paraxial.io is a Gold Sponsor, and will be at the conference in-person. I will be giving a talk, “The Elixir Security Roadmap”, on how organizations using Elixir can prevent data breaches, and a training on April 17th, “Elixir Application Security”.
You can sign up for the training now by clicking here and selecting in-person training ticket. If you are attending ElixirConf make sure to stop by the Paraxial.io booth and say hello. If you would like to schedule a meeting during conference, connecting on LinkedIn is the best way to get in touch. Attending remotely? My calendar is always open if you would like to chat.
Security Vendors and Elixir Support
Michael Lubas, 2024-02-28
Many security vendors claim to support Elixir, yet when setup time comes the results are often disappointing. The chart above lists several common security tools and requirements for securing Elixir code, mapping features to the relevant vendors. Below are notes about how each vendor was assessed. Author contact: michael at this domain.
Introducing Paraxial.io License Scan
Michael Lubas, 2024-02-14
Paraxial.io can now manage open source license compliance for Elixir applications. If your business regulates which licenses are allowed, or simply requires this information be recorded, Paraxial.io now automates this work. There is a serendipitous feature of this release: a dependency inventory can be obtained at compile time instead of runtime.
Consider the following use cases:
Securing Elixir: The Why and How of Paraxial.io
Michael Lubas, 2024-02-07
When a web application is deployed on the internet, it is immediately going to be attacked. Businesses and organizations that rely on these apps have to safeguard the customer information and financial transactions flowing through them every day. Data breaches are a financial and legal nightmare that can be prevented.
This is the problem Paraxial.io solves, preventing data breaches by securing Elixir and Phoenix web applications. Security work should be automated and built into the development process, with tools that communicate risks and remediation paths in clear language. Using Paraxial.io does not require you to be a security expert, the target audience is developers and executives seeking to prevent security incidents.
Secure Asset Management in Elixir with Paraxial.io
Michael Lubas, 2024-01-24
In March 2017 an important security patch for Apache Struts was released, due to a vulnerability with public examples showing how to break into a running server. Apache Struts is to Java what Rails is to Ruby, and Phoenix is to Elixir. Equifax, a major credit bureau, did not have an inventory of every server running Apache Struts, and in May 2017 the highest profile breach ever began with a hacked web server, ending with a $425 million settlement.
When news of a critical security problem becomes public, suddenly the number one priority of an organization’s security team is finding the web facing servers running the vulnerable code, then patching them before an attacker gets in. Proper defense requires a comprehensive inventory of your apps. This is an important milestone, I ranked it number one in the publication Elixir Security Roadmap: A CTO Level Guide because it is the foundation of an effective security program. For many organizations this work is not a high priority until it is too late.
Introducing Paraxial.io Email Reports
Michael Lubas, 2024-01-17
Paraxial.io continuously monitors your Elixir application, ensuring it is safe and free of security vulnerabilities. Today Paraxial.io can now send a weekly summary right to your inbox, keeping you informed on the security of your organization.
Introducing Paraxial.io Slack Alerts
Michael Lubas, 2024-01-10
Paraxial.io monitors your application 24/7, detecting and blocking attacks. When an exploit attempt fails or a bot attack is blocked, it is a noteworthy event. Someone is attacking your work, and Paraxial.io kept it safe. Today you can now receive a Slack notification when this happens.
Consider a remote code execution (RCE) exploit, the type that led to Equifax being hacked. When Paraxial.io detects and stops this attack, you get a notification:
Introducing the Paraxial.io GitHub App
Michael Lubas, 2024-01-03
Modern software development means code changes are pushed into production on a daily basis. A traditional penetration testing engagement provides a snapshot of an application’s security. True security requires automation, where every new change is analyzed.
Elixir has excellent open source security tools, including Sobelow for code security. Why is Paraxial.io needed? Consider the following Sobelow findings:
Webinar Recording: Introducing Paraxial.io 2.0
Michael Lubas, 2023-12-20
The webinar Introducing Paraxial.io 2.0 is live on the Paraxial.io YouTube channel:
Introducing Paraxial.io 2.0
Michael Lubas, 2023-12-06
Today Paraxial.io 2.0 is live, delivering major improvements to help you secure your Elixir and Phoenix applications. How many internet facing Elixir apps do you currently have? When was the last time each one received a security scan? How many critical and high vulnerabilities are outstanding? Paraxial.io makes the complex task of understanding your security posture simple.
Elixir Security Roadmap: A CTO Level Guide
Michael Lubas, 2023-11-15
This document is to help you prevent a data breach due to your Elixir web application being hacked. It covers strategic and technical work that is the most relevant for organizations using Elixir and Phoenix. Get your copy - https://paraxial.io/roadmap
Elixir Security: A Business and Technical Perspective
Michael Lubas, 2023-11-14
My talk from ElixirConf 2023, Elixir Security: A Business and Technical Perspective, is up on YouTube. There are several security benefits to using Elixir, yet these are not very well known in industry. This talk can be used to introduce Elixir to a broader audience. It also covers techniques for securing your own code.
Thinking Elixir 173: Web App Security Best Practices and Sobelow
Michael Lubas, 2023-10-18
Thank you to the Thinking Elixir podcast for having me as a guest for Episode 173: Web App Security Best Practices and Sobelow. Listen and make sure to subscribe on your podcast app.
Elixir Security: Real World Sobelow
Michael Lubas, 2023-10-04
Sobelow is the best static code analysis security tool for Elixir and Phoenix. If you are using Elixir in production today, it is highly recommended that all code is scanned with Sobelow, because it can detect critical vulnerabilities that lead to data breaches. This check is a requirement in many regulated industries, including finance and healthcare. Getting started with Sobelow is easy, using it effectively requires some work. Your first Sobelow scan will likely result in a high number of findings, some of which are false positives. Classifying all these findings is a significant project, daunting enough to stop many businesses from taking full advantage of Sobelow’s power.
The goal of this article is to provide a guide for effectively using Sobelow. It will cover project planning, classifying findings, and using Sobelow effectively. Academic and business writing tends to use “we”, I’m going to use “I” in this article because I have very personal experience with Sobelow. I’ve used it while working as a security engineer, and contributed to the project. The company I started, Paraxial.io, helps people use Sobelow effectively. The adoption of Elixir at many companies was made possible due to Sobelow. Without static security analysis, hundreds of Elixir jobs would not exist. It’s a fantastic security tool, and I hope my experience will help you use it effectively.
Elixir/Phoenix Web Security Guide Released by EEF
Michael Lubas, 2023-09-21
Web Application Security Best Practices for BEAM Languages is a new document from the Erlang Ecosystem Foundation’s (EEF) Security Working Group, published September 5, 2023. It provides guidance for writing secure web applications with Elixir and Phoenix. The document is hosted on the Security WG site, alongside the Elixir Secure Coding and Deployment Hardening Guidelines. Feedback on this new release is welcome, open an issue or submit a PR via Github.
Interview with Michael Frew, Owner of Gigalixir
Michael Lubas, 2023-09-12
Gigalixir is a platform as a service created for Elixir and Phoenix. Launched in 2017 by Jesse Shieh, the service is loved by Elixir developers and businesses alike. In December 2021, Michael Frew acquired Gigalixir from Jesse, becoming the new owner and operator.
Lubas: Michael, great to have you on today. To give readers some context, what’s your professional background?
Elixir Saves Pinterest $2 Million a Year In Server Costs
Michael Lubas, 2023-08-28
The Elixir programming language is well known in the world of software where uptime is critical to business success. The official description states, “Elixir is a dynamic, functional language for building scalable and maintainable applications.” This is a humble summary of the enormous power Elixir contains, which has saved businesses millions of dollars per year across industries.
The book “Adopting Elixir, From Concept to Production (2018)” by Ben Marx, José Valim, Bruce Tate is an excellent guide to the strategic and technical reasons to use Elixir in your business. The very first chapter clearly illustrates the benefits.
Elixir is (Still) Safe
Michael Lubas, 2023-07-24
In March 2021 Nathan Long published Elixir is Safe, a post about the security benefits of using Elixir, which focused on memory and thread safety. It is an excellent article for programmers and executives about the security benefits of Elixir. In July 2023 I googled “Elixir is Safe”, and the first result was a snippet from the paper, “Vision for a Secure Elixir Ecosystem: An Empirical Study of Vulnerabilities in Elixir Programs”, which was published by the ACM in April 2022.
Paraxial.io @ ElixirConf 2023
Paraxial.io, 2023-07-17
ElixirConf US 2023 is happening in Orlando, Florida on September 5th. Paraxial.io is excited to be a sponsor, and to provide security for the conference website. Our founder Michael Lubas is speaking and giving a training on Elixir security. Elixir is a fast growing ecosystem, and ElixirConf provides an important venue for developers, business leaders, and people learning Elixir to network and create meaningful connections. Make sure to stop by the Paraxial.io sponsor booth and say hello!
Inspecting Elixir Dependencies at Runtime for Security
Michael Lubas, 2023-07-05
A common pattern in vulnerability response is that a library has a bad security problem, and you want to check what version is running in production. The syntax of most dependency specification files (including Elixir’s mix.exs) means the exact version running cannot be determined from the file alone. Consider a library where 2.0.3 is not vulnerable, but 2.0.4 is. The project’s mix file has "~> 2.0.0", meaning ">= 2.0.0 and < 2.1.0". The reply to “Are we vulnerable right now?” is an uncomfortable “Maybe, there’s not enough information here”.
Even worse, the security team may decide to search through source code repos (Github, Gitlab, etc) for the relevant library. No matches are found but the vulnerability is present, because it is a sub-dependency of a dependency. While the mix.lock for an Elixir project may be in Github, there is no guarantee that file matches what is running in production.
How to Learn Elixir Security, Curiosum Meetup Talk
Michael Lubas, 2023-06-20
Security is critical for businesses using Elixir in production. There are many resources available to learn more about Elixir security, however it can be difficult to decide where to start. Learn more about this important topic by watching How to Learn Elixir Security from the Curiosum Elixir meetup. YouTube: https://www.youtube.com/watch?v=3STSwMOivQA
Exploit Guard: Open Source Runtime Application Self Protection for Elixir
Michael Lubas, 2023-06-12
Today Paraxial.io is excited to announce Exploit Guard, which adds runtime application self protection (RASP) to Paraxial.io Application Secure. This feature allows businesses using Elixir in production to detect and stop hacking attempts at runtime. The 2017 Equifax data breach started due to a remote code execution (RCE) vulnerability in Apache Struts, a Java framework. This incident resulted in a $425 million dollar settlement, and prompted businesses executives to begin asking questions about application security. Exploit Guard blocks RCE attacks in Elixir.
Exploit Guard is also being published as an open source library, to support the Elixir community. Paraxial.io is grateful to all the hard working, talented Elixir developers in open source, and hopes this library is a positive contribution to the ecosystem.
Phoenix Application Security - ElixirConf 2023 Remote Training
Paraxial.io, 2023-05-24
When deploying your Phoenix application, it seems like there is a never ending list of security problems to worry about. XSS, CSRF, RCE, timing attacks, the list of acronyms and jargon goes on. How should you get started securing your Phoenix app? What is worth focusing on? This training will be an introduction to the web application security concepts most relevant to Phoenix applications, common vulnerabilities, and recommended best practices. This training is fully remote, September 1, 2023.
Private training for businesses is also available, please contact us.
How Elixir Solves a Difficult Security Problem
Michael Lubas, 2023-05-03
The authentication mechanism had been subject to numerous design reviews and penetration tests. The owners were confident that no feasible means existed of attacking the mechanism to gain unauthorized access.
In fact, the authentication mechanism contained a subtle flaw. Occasionally, when a customer logged in, he gained access to the account of a completely different user, enabling him to view all that user’s financial details, and even make payments from the other user’s account. The application’s behavior initially appeared to be random: the user had not performed any unusual action to gain unauthorized access, and the anomaly did not recur on subsequent logins.
Elixir Security: A Guide to Fixing Sobelow Findings
Michael Lubas, 2023-04-24
Sobelow is the static analysis tool for finding security issues in Elixir and Phoenix code. If you’re using Elixir in production, running Sobelow is highly recommended, because it automatically checks for common security issues. Today, detailed guidance on how to triage, verify, and fix each finding is included in Paraxial.io Application Secure. Enterprise customers can also request professional assistance when fixing reported vulnerabilities. This guide is open source, for the benefit of the Elixir community, on the Paraxial.io Github - https://github.com/paraxialio/sobelow_guide
Consider the following Sobelow finding in Paraxial.io Application Secure:
Elixir Security: What's the impact of DoS due to atom creation?
Michael Lubas, 2023-04-05
In Elixir and Erlang, the atom is a basic type, a constant whose value is its own name. There is a hard limit on the number of atoms that can be created, the default is 1_048_576. If external user input results in atoms being created at runtime, this can cause the entire system to crash. There is an obvious question raised from all this, “If my application is vulnerable, what is the impact?”
Will your entire site go down? Could it just crash and restart? The answer depends on the environment your application is running in. The example test below is a Phoenix application running on an AWS EC2 server, using Elixir releases, with systemd.
Elixir Security: Sobelow 0.12.1 Released, Adds LiveView Support
Michael Lubas, 2023-03-30
Sobelow version 0.12.1 was released recently, adding support for HEEx templates, which are used in Phoenix LiveView. Sobelow is a static analysis tool for finding security issues in Elixir and Phoenix code. If you’re using Elixir in production, running Sobelow is highly recommended, because it automatically checks for common security issues.
Note: 0.12.1 is recommended over 0.12.0, because of an issue with castore.
Fast IP Address Matching in Elixir with Radix Trees & Persistent Term, Code BEAM America 2022
Paraxial.io, 2023-03-29
Continue ReadingElixir/Phoenix Security: What is CSRF via Action Reuse?
Michael Lubas, 2023-03-28
The typical description of cross site request forgery (CSRF) involves a POST request being triggered without a secure token. If there’s a state changing HTML form making a POST, with a CSRF token, that’s validated by the server, that should be secure. Consider a web application where both a GET and POST request can perform the same state changing action. This is likely not the developer’s intention, but that is the root of most security problems in software.
Is CSRF possible with a GET request? Yes, in fact it’s worse than a POST request, because GET requests should never be used to perform state changing actions in a web application (place an order, transfer money, etc). The Sobelow finding Config.CSRFRoute: CSRF via Action Reuse states:
Announcing Potion Shop - An Open Source Vulnerable Elixir/Phoenix App for Security Education
Michael Lubas, 2023-03-21
Potion Shop is a Phoenix application vulnerable to common web security issues, such as RCE, XSS, and CSRF. Software developers interested in learning more about Elixir security can examine the source code and functionality of Potion Shop, to better understand how these vulnerabilities occur in a Phoenix project.
Interview with Holden Oullette: Elixir Security, the Sobelow Project, and Scaling Developer Education
Michael Lubas, 2023-03-06
Michael: Hi Holden, what are you currently working on? How is it related to Elixir?
Holden: Hey there! Currently I operate as the Security Architect at Podium where I help our various security teams build out the future of security for a rapidly growing SaaS business which caters to local businesses around the globe.
Elixir/Phoenix Security: Remote Code Execution and Serialisation
Michael Lubas, 2023-02-28
In a Phoenix application, is the code :erlang.binary_to_term(user_input, [:safe]) secure? The answer is no, as the Erlang documentation states, “The safe option ensures the data is safely processed by the Erlang runtime but it does not guarantee the data is safe to your application. You must always validate data from untrusted sources.” Unsafe usage of binary_to_term/2 can lead to a remote code execution (RCE) vulnerability in your application. This means an attacker sends a string of input, which executes malicious code on your production server.
Paraxial.io on Elixir Mix Episode 208: How To Secure Your Elixir Application With Michael Lubas
Paraxial.io, 2023-02-24
Elixir/Phoenix Security: Rate Limits for Authentication with Hammer
Michael Lubas, 2023-02-22
Phoenix applications with user accounts share a common set of features: a login page, account creation, and password reset via an email. These systems are exposed to bot attacks, and developers should be aware of the risks that the public internet imposes on their software. This article will show a risk assessment of a Phoenix application’s login system, and how to use the Hammer library to rate limit the number of requests to each endpoint based on IP address.
Elixir/Phoenix Security Live Coding: Preventing SQL Injection in Ecto
Michael Lubas, 2023-02-16
Learn how to prevent SQL injection in Elixir/Phoenix applications during this live coding webinar. The founder of Paraxial.io, Michael Lubas, will walk through an example Phoenix application, showing secure and insecure Ecto code examples, and how an SQL injection attack works.
YouTube Recording - https://www.youtube.com/watch?v=O5PJcYPC2Lo
Why Does Paraxial.io Focus on Elixir Security?
Michael Lubas, 2023-02-15
Paraxial.io is an application security platform created for Elixir. The two primary use cases are defense against malicious web bots and vulnerability management. Similar tools on the market today include reCaptcha, Snyk, and Cloudflare bot defense. Paraxial.io’s backend is written in Elixir, all our customers are using Elixir, and even this blog is a Phoenix application running Dashbit’s NimblePublisher.
The business focus on Elixir is distinctive, and goes against the conventional wisdom to support as many languages, web servers, and platforms as possible. When security companies lack a clear direction for their product, quality visibly suffers. The unfortunate reality of many vendors is they put shipping any integration possible ahead of a quality product. Paraxial.io has an ambitious goal, the creation of security product that customers enjoy using. This goal, like our focus on Elixir, is unorthodox for a security company.
What is Paraxial.io? A CTO Level Introduction
Michael Lubas, 2023-02-04
Paraxial.io is an application security platform designed for Elixir and Phoenix. We provide an alternative to tools such as Snyk, reCaptcha, and Cloudflare bot defense. You may have questions about these statements, such as, “Why do businesses buy this software?”.
Every business using Elixir and Phoenix in production today needs strong security. Cyber attacks are a daily occurrence on the internet, and criminals are always looking for ways to exploit your business via credit card fraud, credential stuffing, or SMS toll fraud. Building custom solutions to all these problems is extremely costly, and allocates valuable engineering hours away from revenue generating work. Therefore, many businesses choose Paraxial.io, to defend against these attacks.
Elixir Dependency Security: Mix, Hex, and Understanding the Ecosystem
Michael Lubas, 2023-01-24
Dependencies in a software project are a frequent source of security concern. The ability to detect outdated packages, and update to the latest version without breaking the project, is necessary for modern teams. In Elixir, dependencies are hosted by the Hex package manager, and managed by the Mix build tool. To better understand the ecosystem, let’s examine the different components in detail.
Announcing Vulnerability Scanning and Management for Elixir
Paraxial.io, 2023-01-05
Paraxial.io now supports vulnerability scanning and management for Elixir applications. This is done via a mix task, which can be integrated into your CI/CD pipeline, that uploads the result of each scan to the Paraxial.io backend for tracking and reporting. This fulfills the compliance requirements for a number of security standards, and gives your team actionable metrics on the security of your project.
There are three popular security tools for ensuring the security of Phoenix applications:
Rocket Validator Stops Spam Users with Paraxial.io
Paraxial.io, 2023-01-04
Rocket Validator helps website owners detect accessibility and HTML issues in their pages. The founder, Jaime Iniesta, was dealing with an annoying problem: spam user registrations. Bots would register for the service, but these signups were spam, not real humans. Jaime decided to create a Paraxial.io account, and create honeypot forms for the bots to submit. What happened next?
Elixir/Phoenix Security: Denial of Service Due to Atom Exhaustion
Michael Lubas, 2023-01-03
In Elixir, the atom is a basic type, a constant whose value is its own name. Atoms are often hard-coded, meaning the atom :red appears in source code, and is not dynamically created at runtime or compile time. However, it is possible for your application to accept user input, then create a new atom based on that input, for example:
Paraxial.io on Thinking Elixir Episode 131: Start Securing Elixir and Phoenix
Paraxial.io, 2022-12-28
Elixir/Phoenix Security: How attackers bypass IP based rate limiting
Michael Lubas, 2022-12-20
“Limit the number of login attempts for one IP address to 5 in a 30 second period” is a standard rule for many web applications, and makes sense from the perspective of a site owner dealing with malicious credential stuffing. With the rise of cloud computing, it has become much easier for an attacker to access thousands of different IP addresses, for free, to bypass IP based blocking. This article will use a Phoenix application to demonstrate what the attack looks like, and how Paraxial.io stops it.
Betafi Blocks Bots on Launch Day with Paraxial.io
Paraxial.io, 2022-12-05
Betafi is a user research platform that makes it easy to capture and make sense of customer feedback sessions. User interviews, usability testing, and sharing business insights are all supported. Built on Elixir and Phoenix, the team at Betafi was preparing to launch on Product Hunt, and wanted to ensure the big launch day was not disrupted by bot attacks.
Elixir/Phoenix Security: Introduction to Cross Site Request Forgery (CSRF)
Michael Lubas, 2022-12-05
Cross site request forgery (CSRF) is a type of vulnerability in web applications, where an attacker is able to forge commands from a victim user. For example, consider a social media website that is vulnerable to CSRF. An attacker creates a malicious website aimed at legitimate users. When a victim visits the malicious site, it triggers a POST request in the victim’s browser, sending a message that was written by the attacker. This results in the victim’s account making a post written by the attacker.
How does this work in practice? This article will use a basic Phoenix application, vulnerable to CSRF, to show what the attack looks like. Phoenix provides you with excellent defaults to prevent CSRF, which have been removed for this exercise. After the vulnerability has been covered, we will examine how Phoenix prevents CSRF by default.
Announcing Elixir and Phoenix Security Consulting Services
Michael Lubas, 2022-11-16
As Elixir and Phoenix adoption continues to increase in industry, the need for security expertise has grown as well. Finding engineers with a deep understanding of the Elixir ecosystem, and software security, is a difficult task.
Today we are announcing our Elixir and Phoenix focused security consulting services. No more worrying if the firm you are working with has anyone familiar with Elixir. Visit the consulting page on our website for the full list of services. If you have questions or want to get started, click here to schedule a call.
Securing Elixir/Phoenix Applications: 5 Tips to Get Started
Michael Lubas, 2022-11-16
There are a number of resources online related to Elixir and Phoenix security, however when it comes to securing your own project, determining where to begin is a difficult task. Here are five recommendations to get started improving the security of your application.
Cross Site Scripting (XSS) Patterns in Phoenix
Michael Lubas, 2022-10-24
Cross Site Scripting (XSS) refers to a class of vulnerability in web applications, where an attacker is able to inject a script into the browsing context of a victim. The root cause of this vulnerability is untrusted user input being rendered in a web browser, where JavaScript written by an attacker is executed. If a website has user authentication, and an attacker is able to exploit XSS in the site, the end result is user accounts will be compromised.
Phoenix provides strong guard rails to prevent developers from introducing XSS into their application, however it is possible to bypass these protections and write insecure code. This article will use the Phoenix application cross to demonstrate what vulnerable code looks like. The source code for cross is posted on GitHub.
Detecting SQL Injection in Phoenix with Sobelow
Michael Lubas, 2022-10-06
SQL injection is a type of attack against a web application, where some malicious input is parsed by the underlying database, resulting in an unauthorized operation being performed. This can be the disclosure of sensitive data, modification of the database, or deletion of entire tables.
Most Phoenix applications use Ecto, a database wrapper and query generator for Elixir. When used correctly, Ecto prevents SQL injection due to the way queries are constructed. For example, the Ecto query
Elixir code style, a brief example
Michael Lubas, 2022-09-14
Write a function in Elixir named build_string that takes 4 arguments:
ElixirConf 2022 Teller Challenge Writeup
Michael Lubas, 2022-09-06
At this year’s ElixirConf Teller hosted a challenge in Elixir, write an Elixir client for a banking application to get the secret account number and balance. This is a writeup for the remote attendee instance, if you played this in-person at ElixirConf the setup was different.
After signing up for an account you land on this page:
Setting User-Agent in Elixir with Finch, HTTPoison, Req, or Tesla
Michael Lubas, 2022-08-17
In 1996 Google co-founder Larry Page posted in comp.lang.java, Q: Setting User-Agent Field?. 26 years later, you may still need to set the User-Agent in your project. Here are four examples from the Elixir HTTP clients Finch, HTTPoison, Req, and Tesla.
The above screenshot is from Paraxial.io, which shows the User-Agent of incoming HTTP requests to a Phoenix application. If you don’t have an account use ngrok to verify what User-Agent you’re sending.
eBook Release: Inside a Web Bot Attack 🤖
Paraxial.io, 2022-08-10
It was an ordinary day at work for Peter, until he saw a spike in login attempts 1,000 times higher than average! Go inside the response to a bot attack and learn how Paraxial.io can keep your business secure.
Paraxial.io Featured in ElixirCasts Episode 149
Paraxial.io, 2022-08-05
Paraxial.io was featured in the excellent ElixirCasts, a series of video tutorials on Elixir and Phoenix. The episode walks through the installation of Paraxial.io in less than seven minutes, and the configuration of a rule to stop automated credential stuffing attacks.
Testing a Phoenix application for credential stuffing with Elixir, Floki, and HTTPoison
Michael Lubas, 2022-07-14
Credential stuffing is a type of attack performed against web applications, where the attacker uses username/password pairs from a data breach as input to a program, which performs automated login attempts against a victim application. This is a highly effective technique for stealing user accounts, because password reuse is so common.
This post will demonstrate how to test a Phoenix web application to see if credential stuffing from one IP address is possible. If you work on a public-facing web application, and want to improve its security, this is an excellent test. Credential stuffing attacks are easy for attackers to perform, and lead to user accounts getting compromised. If you currently have defenses in place, such as a bot prevention tool, captcha, or custom plugs, this project will reveal discrepancies between how you expect the system to behave, and how it actually does.
🎉 Announcing the Paraxial.io Beta Launch! 🎉
Paraxial.io, 2022-05-28
Paraxial.io protects your Elixir/Phoenix application from bots attempting automated logins, scraping, and disruption of service. Today we are happy to announce the beta program is open to new users!
To sign up, email support@paraxial.io with a brief description of your website, and you will receive a reply within two days.
Classifying Data Center IP Addresses in Phoenix Web Applications with Radix Trees
Michael Lubas, 2022-05-10
Several cloud hosting companies publish the IP address ranges of their services. Examples include AWS, Azure, GCP, Oracle, and DigitalOcean. This information is useful to website owners, because the expected behavior of a client coming from a cloud server is different from a residential IP address. Consider a website that sells concert tickets, and wants to prevent bots from quickly purchasing all available tickets. The website owner notices that when tickets go on sale, hundreds of clients with data center IP addresses are making automated requests, purchasing tickets for resale before real visitors can.
This tutorial will demonstrate how to classify incoming requests to a Phoenix web application. This is based on a comparison of the request’s IP address with a data structure containing the IP ranges of several cloud providers. It will cover:
Throttling and Blocking Bad Requests in Phoenix Web Applications with PlugAttack
Paraxial.io, 2022-02-02
Web applications that accept username and password pairs for authentication may experience credential stuffing by malicious clients. We use the term “credential stuffing” to refer to the act of using credentials, taken from a website’s public data breach, to preform many authentication attempts against victim accounts on a different website. This tutorial will demonstrate how to mitigate credential stuffing against a Phoenix Framework application, using PlugAttack.